Medicare under attack: Healthcare data breaches increase fraud risks

Medicare under attack: Healthcare data breaches increase fraud risks

Thieving Medicare beneficiary identification figures has grow to be the latest aim for cybercriminals who see this facts as even additional useful than stolen credit cards

A South Florida guy pled responsible in federal court in late-January to “conspiring to get and offer extra than 2.6 million Medicare beneficiary identification numbers” and other own data. His responsible plea was one of the to start with prosecutions beneath the Medicare Accessibility and CHIP Reauthorization Act of 2015, which makes it “illegal to buy, provide, or distribute Medicare beneficiary identification numbers without having proper authority.”

As portion of his plea, the defendant admitted he and his co-conspirators used “data mining” and “social engineering techniques” to gather Medicare beneficiary info that he then marketed and offered online. The defendant bought the Medicare figures and other information of 83,000 beneficiaries to undercover federal agents for $8,000, in accordance to courtroom documents. The governing administration estimates he designed about $310,000 for transactions involving hundreds of thousands of Medicare beneficiary identification figures.

Medical identity theft, like the theft of Medicare beneficiary identification figures, normally supports the filing of untrue statements for Medicare reimbursement that can price tag the federal authorities billions of dollars a year in taxpayer funds.

Cybersecurity attacks on health care companies “reached an all-time substantial, with a single analyze indicating that a lot more than 45 million folks have been affected by these kinds of assaults in 2021” — a 32{35112b74ca1a6bc4decb6697edde3f9edcc1b44915f2ccb9995df8df6b4364bc} increase above 2020 — in accordance to a U.S. Senate Intelligence Committee white paper introduced in November 2022. Assaults on healthcare companies are expanding due to the fact private wellbeing facts “is a lot more valuable on the black market” than credit rating card facts. Hackers can offer health-related information for $10 to $1,000 for every document, according to the white paper.

The scale of info breaches in healthcare is sweeping. In calendar calendar year 2021, the Office of Civil Legal rights (OCR) for the U.S. Department of Health and fitness and Human Providers gained 609 notifications of breaches impacting 500 or extra people that uncovered the secured wellness information of additional than 37 million people today. An added 319,000 folks experienced their facts uncovered in more compact breaches, according to the OCR’s report produced in mid-February.

Breach hazards cross the spectrum

Even though social engineering can expose unique Medicare beneficiaries to establish theft, health care vendors are also the victims of facts breaches from ransomware assaults, hacking, and even worker error. Being aware of the threats and having steps to mitigate those dangers can aid decrease facts breaches and the health care fraud that can follow.

However, hacking is the dominant danger for healthcare information breaches with hacking and “IT incidents” associated in 75{35112b74ca1a6bc4decb6697edde3f9edcc1b44915f2ccb9995df8df6b4364bc} of reportable breaches. For case in point, Banner Wellbeing Affiliated Lined Entities agreed to fork out $1.25 million to solve a 2016 data breach that “disclosed the protected overall health information and facts of 2.81 million shoppers,” according to a February OCR release, which termed the information breach the result of a “hacking incident by a menace actor.”

“Hackers continue on to threaten the privacy and protection of affected individual info held by well being treatment businesses, together with our nation’s hospitals,” mentioned OCR Director Melanie Fontes Rainer. “It is critical that hospitals and other coated entities and business enterprise associates be vigilant in having strong methods to secure their devices, facts, and data, and this starts with comprehension their threats, and getting action to prevent, reply to, and battle such cyber-attacks.”

The U.S. Department of Justice announced in January that it had productively disrupted the operations of the Hive ransomware team, which had qualified more than 1,500 victims in additional than 80 nations close to the world, together with hospitals, faculty districts, financial companies, and essential infrastructure. A suspected Hive assault on an Ohio health and fitness method resulted in the cancellation of all urgent surgical scenarios and radiology examinations as effectively as the diverting of unexpected emergency sufferers prior to reaching a “negotiated solution.”

Third-get together suppliers can also create a knowledge breach vulnerability for vendors. UCHealth in Aurora, Colo. documented a 3rd-celebration info breach that impacted approximately 49,000 men and women. UCHealth explained it was educated by the company delivering hosted services to the health method that the software package company experienced expert a stability incident that may have uncovered some of UCHealth’s affected individual, provider, or employee details. Despite the fact that UCHealth’s units, which includes its electronic health data, were being not impacted by the incident, it furnished a discover of the breach to persons that the data downloaded may possibly have provided names, addresses, dates of birth, cure info, and, in limited situations, Social Protection quantities or other monetary info. On the other hand, UCHealth did not think the data taken “went over and above the cybercriminal or was misused in any way.”

Data sharing risks

Unintended data sharing can also outcome in considerable exposures of overall health information and facts. UCLA Health and fitness introduced in mid-January, that it experienced “recently realized of an difficulty relating to the use of analytics applications on the UCLA Wellbeing web page and mobile application.” UCLA Wellbeing described that analytics applications on an appointment request variety done on the site or mobile application may perhaps have “captured and transmitted” information from the sort to 3rd-social gathering company vendors. UCLA Overall health notified almost 94,000 folks of the facts breach nevertheless, UCLA denied that analytics resources captured money or payment information and facts from people.

In yet another instance involving data sharing, the Federal Trade Commission filed a grievance from GoodRx Holdings, Inc., alleging GoodRx shared “delicate consumer details” with providers like Fb, Google, and Criteo as well as other 3rd parties. GoodRx did not have authorization from its consumers to share their personal wellbeing info, these as their prescription drugs and personalized health situations, according to the criticism. GoodRx paid a $1.5 million settlement to resolve the allegations, but denied any wrongdoing.

Even so an individual’s health and fitness facts is exposed — no matter if by individual recognize theft, hacking attack, or unintended sharing — when it consists of payment information, it results in a hazard of health care fraud. Despite the fact that Medicare figures are bought and sold on the darkish internet in bulk, any disclosure of payment information and facts can boost the hazard of particular person or systemic fraud.

California medical group discloses ransomware attack, more than 3 million affected

California medical group discloses ransomware attack, more than 3 million affected

Regal Healthcare Team, based in southern California, explained the breach occurred in December 2022.

A clinical group primarily based in southern California reported it was hit with a ransomware attack that has likely uncovered the personal overall health information of people.

Regal Health-related Group posted the info on its website Friday. Far more than 3.3 million persons may possibly be afflicted, in accordance to a submitting with the U.S. Section of Overall health & Human Services’ Business office of Civil Legal rights. Health care companies are needed to report any knowledge breach affecting at least 500 people today to the federal govt.

Regal claimed the breach, which it explained originated from a “ransomware cyberattack” happened on or about Dec. 1.

The breach could have exposed info from Regal and its affiliate marketers: ​​Lakeside Clinical Corporation, Affiliated Medical professionals of Orange County and Higher Covina Professional medical Group.

“On Friday, December 2, 2022, Regal staff found issues in accessing some of our servers,” Regal stated in a put up on its web site. “After intensive evaluation, malware was detected on some of our servers, which a threat actor utilized to entry and exfiltrate information.”

“We employed 3rd-celebration sellers knowledgeable in this spot to guide with our reaction to the incident. The Regal staff labored with the suppliers to effectively restore accessibility to our techniques and to analyze the impacted facts,” the healthcare team explained.

Client data that could have been uncovered features names, Social Security figures, dates of start, cellular phone quantities, prognosis and cure data, wellbeing approach member quantities, prescriptions and lab benefits, Regal mentioned.

The clinical group said it is bolstering security protocols, and is featuring no cost credit score checking to patients for a person year. Clients with Regal can simply call the health-related group at 866-918-5293.

Scores of hospitals and health programs have been hit with ransomware assaults. Overall health programs have a prosperity of precious affected individual facts, and terrible actors have realized that hospitals and healthcare organizations will pay back ransoms to restore techniques, cybersecurity experts say.

A lot more health care organizations say they are dealing with ransomware assaults, and they are owning an influence on client care.

In a survey of healthcare IT gurus introduced by the Ponemon Institute last thirty day period, approximately 50 percent (47{35112b74ca1a6bc4decb6697edde3f9edcc1b44915f2ccb9995df8df6b4364bc}) reported their corporations knowledgeable a ransomware assault in the earlier two decades, up from 43{35112b74ca1a6bc4decb6697edde3f9edcc1b44915f2ccb9995df8df6b4364bc} in 2021. And 45{35112b74ca1a6bc4decb6697edde3f9edcc1b44915f2ccb9995df8df6b4364bc} of respondents documented troubles from professional medical procedures owing to ransomware assaults, up from 36{35112b74ca1a6bc4decb6697edde3f9edcc1b44915f2ccb9995df8df6b4364bc} in 2021.

Federal authorities explained final month they managed to disrupt the Hive ransomware team, which has targeted hospitals and financial organizations. The FBI managed to penetrate Hive’s devices, recover decryption keys and presented those people resources to victims. The FBI’s efforts prevented victims from acquiring to pay back $130 million in ransom payments, the U.S. Justice Section claimed.

Final week, Tallahassee Memorial Health care disclosed what it explained as an “IT safety function,” forcing the organization to get down programs, postpone non-unexpected emergency surgeries, and divert some individuals. Tallahassee Memorial has not explained the incident as a ransomware attack, but it is using paper documentation.

The system reported Thursday that it is making progress in restoring some programs and is commencing to improve its individual load.

“We are now performing towards bringing impacted techniques back on the internet,” Tallahassee Memorial reported. “As is customary with occasions of this character, it will just take some time to return to regular functions. When we can’t share a definitive timeline, we are building important progress and doing work nonstop to convey methods again on-line properly as quickly as doable.”

CommonSpirit Health says some patient information accessed in ransomware attack

CommonSpirit Health says some patient information accessed in ransomware attack

The program stated the breach involved individual facts from Virginia Mason Franciscan Health and fitness, an affiliate of CommonSpirit.

CommonSpirit Well being mentioned some patient information was accessed in a ransomware attack previously this drop.

CommonSpirit, a non-financial gain, Catholic firm, is 1 of America’s major overall health units, functioning 140 hospitals and a lot more than 1,500 care internet sites in 21 states.

The method reported last week that the breach involved affected person information and facts from Virginia Mason Franciscan Wellness, an affiliated entity of CommonSpirit. Letters to people influenced ended up despatched by using U.S. mail on Dec. 1, the system reported.

CommonSpirit claimed another person obtained accessibility to personalized details from Franciscan Wellbeing and/or Franciscan Professional medical Group in Washington point out. An investigation decided that hackers gained accessibility to components of CommonSpirit’s community in between September 16, 2022 and October 3, 2022.

To date, CommonSpirit claimed it has uncovered no evidence that any personalized details has been misused as a consequence of the breach.

Some of the documents had been relevant to people, relatives customers of clients, or caregivers of sufferers and included names, addresses, cellular phone numbers, dates of delivery, and a one of a kind ID used only internally by the organization, CommonSpirit said. The facts did not involve coverage identification figures or healthcare history figures.

CommonSpirit said the facts in the documents linked to clients, kin or caregivers of clients that may perhaps have been found at Washington condition spots which includes: St. Joseph Hospital (Tacoma) St. Francis Clinic (Federal Way) St. Elizabeth Medical center (Enumclaw) St. Clare Hospital (Lakewood) St. Anthony Hospital (Gig Harbor) St. Anne Medical center, previously Highline Hospital (Burien) St. Michael Medical Centre, formerly Harrison Healthcare facility (Bremerton & Silverdale) and physician clinics associated with Franciscan Health.

In the months immediately after the attacks, Virginia Mason Franciscan Wellbeing stated some patient appointments were being rescheduled or canceled. CHI Well being, which is section of CommonSpirit, mentioned it experienced to reschedule some individual appointments and postponed some procedures on a case-by-case foundation.

CommonSpirit mentioned it is working with law enforcement in the investigation. The group said some units have been temporarily taken offline but were being afterwards restored with supplemental stability instruments.

CommonSpirit disclosed an information and facts know-how incident in early Oct and later disclosed the incident was a ransomware attack.

Hospitals and health and fitness methods have been strike by extra ransomware assaults in latest many years. Cybersecurity specialists say hospitals are tempting targets, and irrespective of some improvements, stay as well vulnerable to attacks. Ransomware gangs have also discovered that some hospitals are willing to pay back the ransom, professionals say, even though they suggest towards it.

Thousands and thousands of People have been impacted by breaches involving private health and fitness info this calendar year, in accordance to facts from the U.S. Department of Well being and Human Solutions.

Wellness units are acquiring cyberattacks to be pretty costly. The ordinary health care breach cost $10.1 million, in accordance to an IBM Stability report.

Cyberattacks also threaten the protection of sufferers, specially if digital wellbeing file systems are essential to be taken offline and treatments should be delayed. Marketplace industry experts have urged hospitals to see cybersecurity as necessary to preserving patient security.

Examine far more from Main Healthcare Govt

How hospitals can improve their cybersecurity

How a rural system improved its cybersecurity

DASH diet may be best to reduce heart attack risk

DASH diet may be best to reduce heart attack risk

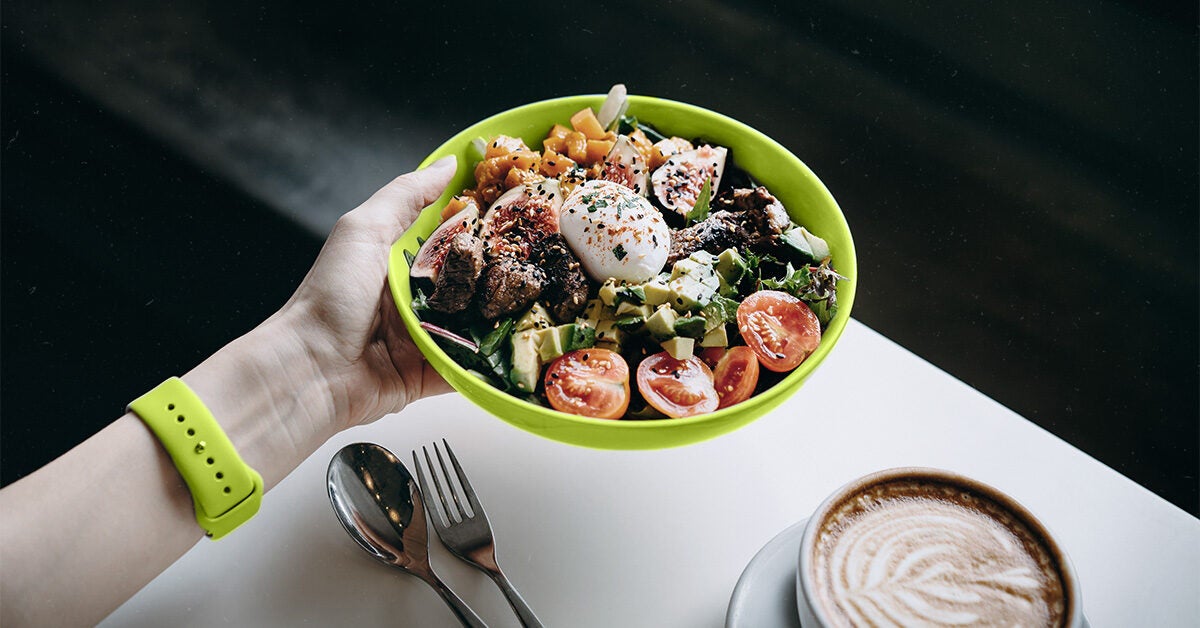
A woman wearing a smart watch holds a bowl full of foods that adhere to the DASH diet above a table with with cutlery and a cup of coffee laid outShare on Pinterest
Following the DASH diet may have cardiovascular benefits for people with hypertension. d3sign/Getty Images
  • Globally, approximately one in three 30–79-year-olds have hypertension — or in other words, high blood pressure.
  • A new simulated study has found that following a DASH diet may be the most effective lifestyle intervention to reduce cardiovascular disease in people with mild hypertension.
  • The study found that this dietary change could prevent nearly 3,000 deaths in the U.S. alone.

The World Health Organization estimates that worldwide 1.28 billion adults ages 30-79 have high blood pressure or hypertension. Two-thirds of them live in low- and middle-income countries. Hypertension can be a deadly condition, causing 7.5 million deaths annually.

Previous research has identified several lifestyle changes that can lower a person’s blood pressure, including dietary changes, regular exercise, and reducing alcohol intake.

A new report finds that for people in the early stages of hypertension, diet — and one diet in particular —stands out as being the most effective means of maintaining healthy blood pressure. The report was presented in early September at the American Heart Association’s Hypertension Scientific Sessions 2022 in San Diego.

According to the new report’s estimate, the DASH diet could avert upwards of 15,000 heart disease events among men and 11,000 among women in the U.S. alone.

The authors of the report conducted a simulation study to assess future hypertension outcomes. About 61{35112b74ca1a6bc4decb6697edde3f9edcc1b44915f2ccb9995df8df6b4364bc} of the modeled population had access to healthcare. Roughly half were women.

Interdisciplinary researcher and educator Dr. Kendra Sims, a postdoctoral fellow at the University of California, is the co-lead researcher of the study. She explained the methodology behind the report to Medical News Today:

“In our case, a simulation consists of pulling in several sources of information, including the Census, that reflect the current and expected changes in the U.S. population.”

“Among the simulated people initially without heart disease, we plug in the risk factors drawn from rigorous research studies on heart attack and stroke events. This method allows us to confidently project the number of people who are likely to develop heart disease over the next decade,” she said.

Blood pressure is when blood exerts outward pressure against the walls of arteries. Hypertension happens when blood exerts a pressure higher than what is thought to be good for arteries.

To measure someone’s blood pressure, healthcare professionals take two readings:

  • The systolic blood pressure measurement records the pressure exerted on artery walls during heartbeats.
  • The diastolic blood pressure measurement records the pressure exerted on artery walls between heartbeats.

Blood pressure is measured in millimeters of mercury — mm Hg — and expressed as the systolic measurement over the diastolic measurement.

The severity of raised blood pressure can be categorized in stages:

  • Elevated — 120-129 systolic/less than 80 diastolic
  • Stage 1 hypertension — 130-139 systolic/80-89 diastolic
  • Stage 2 hypertension — greater than 140 systolic/greater than 90 diastolic
  • Hypertension crisis — greater than 180 systolic/greater than 120 diastolic

Hypertension is sometimes referred to as the “invisible killer.”

“Millions of working-aged people are walking around with elevated blood pressure,” said Dr. Sims, “which is symptomless, but is also a leading preventable cause of disability and death.”

The WHO estimates that 46{35112b74ca1a6bc4decb6697edde3f9edcc1b44915f2ccb9995df8df6b4364bc} of adults with hypertension do not know that they have it.

“Most [hypertension patients] did not follow the recommended DASH diet. Less than two-thirds of them had regular access to healthcare. This was particularly true for men and people between 45 and 54.”
— Dr. Kendra Sims

The study’s model also revealed a troubling surprise.

“We found that young- and middle-aged adults with stage 1 hypertension aren’t as low risk as you — or even your doctor — might think!” she said.

The report predicts that 8.8 million people ages 35-64 have untreated stage 1 hypertension.

The development of the DASH diet began in the 1990s, and it has been refined over the years. “DASH” stands for “Dietary Approaches to Stop Hypertension.”

Dr. Jennifer Wong, medical director of noninvasive cardiology at the MemorialCare Heart & Vascular Institute of Orange Coast Medical Center, who was not involved in the study, explained the cardiological benefits of the DASH diet to MNT:

“The DASH diet promotes foods high in potassium, magnesium, calcium, fiber, and protein [as] these nutrients help lower the blood pressure.”

“[With the DASH diet], there’s also a limiting of sodium that can help lower blood pressure. Sodium is known to pool water into blood vessels, and can increase the blood pressure that way. And we all know that high blood pressure increases the risk of arterial thickening and consequent heart attack, stroke, and kidney failure.”
— Dr. Jennifer Wong

While the DASH diet limits the consumption of saturated fats, meat, and oil, Dr. Wong noted, “And also interesting, I think in addition to an avoidance of certain foods, is its emphasis on increasing certain foods like fruits and vegetables.”

The simulation focused on people who have been diagnosed with mild-to-moderate hypertension. Dr. Wong explained the likely reason:

“That particular group is at a point where you can really prevent problems before they become harder to control. So, you know that early hypertension-elevated, blood pressure group stage 1 hypertension, that’s a group where I think making a difference with lifestyle changes could really go a long way.”

The researchers found that switching to a DASH diet could prevent approximately 2,900 deaths annually, with a reduction in national healthcare costs of $1.6 billion.

Michelle Routhenstein, cardiology dietician at EntirelyNourished.com, who was also not involved in the report, told MNT:

“The examples typically used on the DASH diet may not be culturally sensitive, and they need to be personalized/adapted by a qualified registered dietitian nutritionist for optimal success.”

Routhenstein cautioned: “I find that many people pick and choose certain principles of the DASH diet, which may lead to leaving out a big part of its effectiveness.”

“In order to make a large-scale societal level change,” she added, “more how-to and implementation tips that make it culturally sensitive, applicable, and appetizing for each individual is key.”

Dr. Sims pointed out, “This research reveals that we should look to feasible ways our food system could make healthy eating the default option.”

“This might be as straightforward as lowering the amount of salt in pre-packed food or subsidizing large-scale agriculture to grow fruit and vegetables instead of corn.”
— Dr. Kendra Sims

“Straightforward,” said Dr. Sims, “does not mean simple. Well-being is a full-time, lifelong job. At the same time, financial and social constraints throw up hurdles between millions of people and healthy behaviors.”

“Health providers and policymakers must connect people with solutions instead of blaming them for being sick.”

“This may look,” concluded Dr. Sims, “like providing a list of local farmer’s markets that doubles EBT credits or confirming that someone has a working kitchen to store and prepare food. Above all, it means collaborating with the patient about healthy, delicious choices that fit best into their culture and lifestyle.”